


Own and mature the organization’s DAST program by configuring tools, running authenticated tests against web applications and APIs, integrating testing into CI/CD pipelines, and validating vulnerabilities. The role also performs manual security assessments, threat modeling, code review, and SAST/SCA oversight; guides remediation; supports secure architecture, incident response, compliance, developer education, and executive risk reporting.
Application Security Consultant - DAST
Enterprise Cyber Security
Full Time, Springfield - MA
The Opportunity
We are seeking a highly skilled and experienced Application Security Consultant to advance our application security initiatives, with a particular emphasis on dynamic application security testing (DAST). You will own and mature how we test running applications and APIs for exploitable weaknesses, drive secure development practices, and implement solutions that protect our systems and data from evolving threats. The role partners with development teams, security architects, leadership, and other stakeholders to embed security into every stage of the software development lifecycle.
The Team
Our Application Security team keeps MassMutual's software applications secure through rigorous assessment and proactive development team engagements. We work closely with security architects, DevOps engineers, and software developers, while our core focus is identifying and verifying vulnerabilities - including hands-on dynamic testing of running applications and APIs - implementing security best practices, and helping development teams remediate. Our backgrounds span software engineering to red teaming, and we value continuous learning, innovation, and collaboration.
The Impact
Your key responsibilities will ensure applications are resilient against emerging threats, reducing the financial and reputational damage of security incidents.
The Minimum Qualifications
The Ideal Qualifications
#LI-RK1
MassMutual is an equal employment opportunity employer. We welcome all persons to apply.
If you need an accommodation to complete the application process, please contact us and share the specifics of the assistance you need.
California residents: For detailed information about your rights under the California Consumer Privacy Act (CCPA), please visit our California Consumer Privacy Act Disclosures page.
Salary Range: $137,800-$180,800
Enterprise Cyber Security
Full Time, Springfield - MA
The Opportunity
We are seeking a highly skilled and experienced Application Security Consultant to advance our application security initiatives, with a particular emphasis on dynamic application security testing (DAST). You will own and mature how we test running applications and APIs for exploitable weaknesses, drive secure development practices, and implement solutions that protect our systems and data from evolving threats. The role partners with development teams, security architects, leadership, and other stakeholders to embed security into every stage of the software development lifecycle.
The Team
Our Application Security team keeps MassMutual's software applications secure through rigorous assessment and proactive development team engagements. We work closely with security architects, DevOps engineers, and software developers, while our core focus is identifying and verifying vulnerabilities - including hands-on dynamic testing of running applications and APIs - implementing security best practices, and helping development teams remediate. Our backgrounds span software engineering to red teaming, and we value continuous learning, innovation, and collaboration.
The Impact
Your key responsibilities will ensure applications are resilient against emerging threats, reducing the financial and reputational damage of security incidents.
- Own and advance our dynamic application security testing (DAST) program - selecting, deploying, configuring, and maintaining DAST tooling across our web application and API estate.
- Design and run authenticated dynamic scans against complex applications, including session handling, multi-step workflows, single-page applications, and REST/GraphQL APIs.
- Integrate DAST into CI/CD pipelines and pre-production environments so dynamic testing runs continuously rather than as a point-in-time exercise, and define the thresholds that gate a release.
- Triage, validate, and tune DAST output - eliminating false positives, confirming exploitability through manual verification, and translating findings into actionable remediation guidance for development teams.
- Complement automated dynamic testing with manual techniques to identify, risk-assess, and prioritize application-level vulnerabilities (e.g., OWASP Top 10) that scanners alone do not surface.
- Conduct in-depth security assessments, including vulnerability scanning and code review.
- Conduct detailed threat modeling to identify attack vectors and potential weaknesses, and use the results to focus dynamic test coverage where risk is highest.
- Collaborate with security architects to design secure application architectures aligned to industry best practices, ensuring secure coding practices are followed and security controls are built into software designs.
- Partner with our SDLC Council to develop and maintain secure coding standards that empower developers to integrate security into their own workflow.
- Partner with DevOps teams to implement security controls within CI/CD pipelines for automated, seamless deployment of secure code.
- Maintain the broader application security testing toolchain, including static analysis (SAST) and software composition analysis (SCA), alongside DAST.
- Evaluate third-party software and APIs for security compliance, including dynamic testing of externally sourced components where appropriate.
- Support incident response for application security events, providing rapid identification and mitigation guidance.
- Ensure compliance with applicable security regulations, frameworks, and industry standards.
- Use reporting tools to communicate vulnerability and code-defect risk to MassMutual's cyber assets through metrics (KPIs, KRIs, OKRs), enabling team leaders and executive leadership to make risk-based prioritization decisions.
- Educate developers and stakeholders on secure coding practices and on interpreting and acting on dynamic test results.
- Stay current on security threats, vulnerabilities, and industry trends, and apply them to improve our security strategy.
The Minimum Qualifications
- Bachelor's Degree
- 8+ years of experience in application security, penetration testing, or secure software development.
The Ideal Qualifications
- Deep, hands-on expertise with DAST tooling (e.g., Burp Suite, OWASP ZAP, Invicti, Acunetix, StackHawk) including authenticated scan configuration, scan policy tuning, and API scanning.
- Demonstrated hands-on experience with dynamic application security testing (DAST) of web applications and APIs.
- Experience operationalizing DAST at scale - pipeline integration, scheduled scanning across a large application estate, results triage workflows, and reducing false-positive rates over time.
- Relevant security certifications such as CEH, OSCP, CISSP, or GWAPT from an industry-recognized certifier (e.g., SANS/GIAC, CompTIA, ISACA, ISC2).
- Strong knowledge of secure software development methodologies, including threat modeling, code review, and static/dynamic analysis.
- Deep understanding of common application vulnerabilities (e.g., OWASP Top 10) and their mitigations, with the ability to manually verify and exploit findings to confirm real risk.
- Experience integrating security into DevOps (DevSecOps) and CI/CD environments.
- Strong technical knowledge of web application security, cloud security (AWS, Azure, GCP), mobile security, infrastructure as code, containerized environments (Docker, Kubernetes), and API security.
- Hands-on experience across the wider testing toolchain - SAST, SCA, IAST, and fuzzing tools.
- Experience identifying security defects in container images and Kubernetes environments.
- Advanced proficiency writing source code in at least one programming language (e.g., Java, JavaScript, C/C++/C#, Python) and familiarity with common build and dependency tooling (e.g., Maven, Gradle, Node).
- Experience with cloud deployment and automation tooling (Terraform, GitHub Actions, Jenkins, AWS CloudFormation, secrets managers).
- Working knowledge of encryption, authentication, and access control.
- Knowledge of compliance and regulatory frameworks (e.g., SOC 2).
- Strong analytical and problem-solving ability, with excellent communication skills - able to explain security issues to both technical and non-technical stakeholders.
- A collaborative team player comfortable in a fast-paced environment.
#LI-RK1
MassMutual is an equal employment opportunity employer. We welcome all persons to apply.
If you need an accommodation to complete the application process, please contact us and share the specifics of the assistance you need.
California residents: For detailed information about your rights under the California Consumer Privacy Act (CCPA), please visit our California Consumer Privacy Act Disclosures page.
Salary Range: $137,800-$180,800
MassMutual Boston, Massachusetts, USA Office
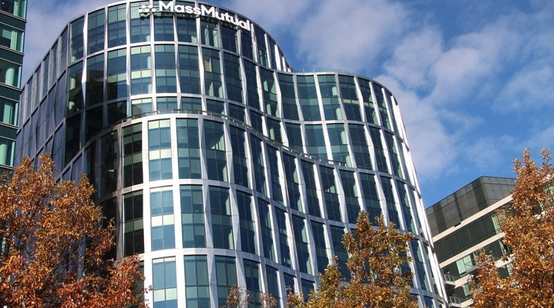
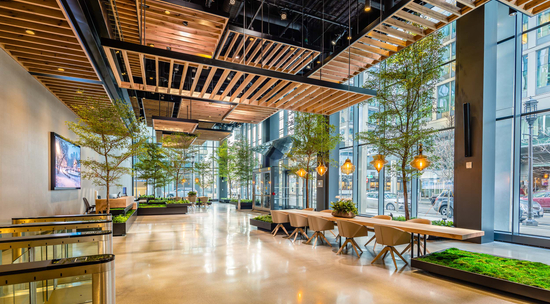
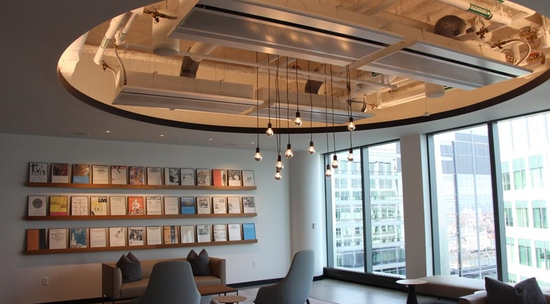
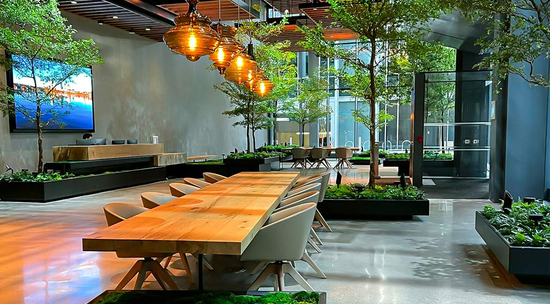
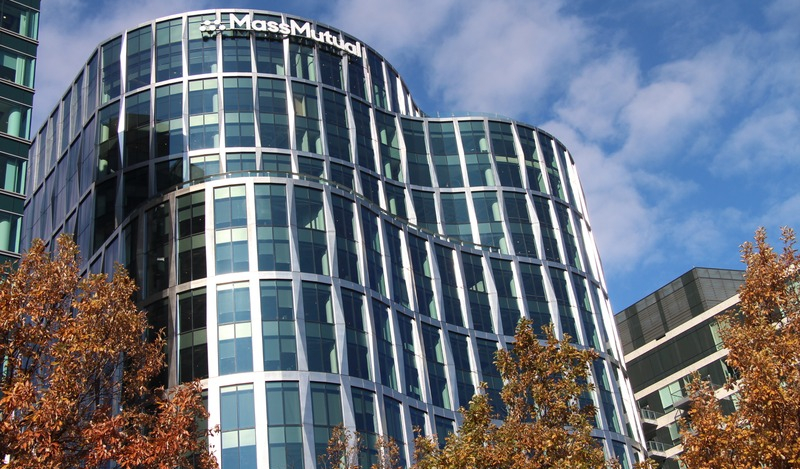
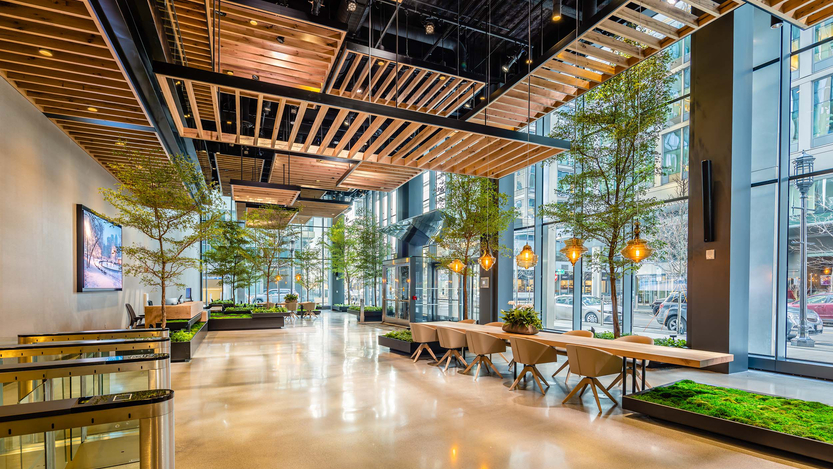
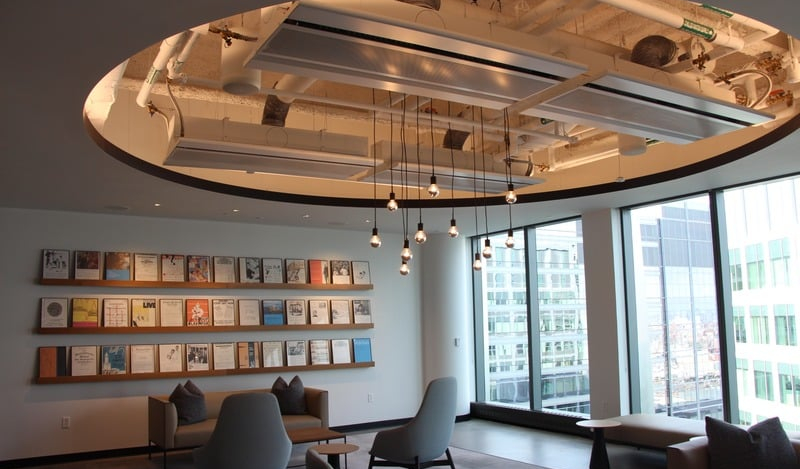
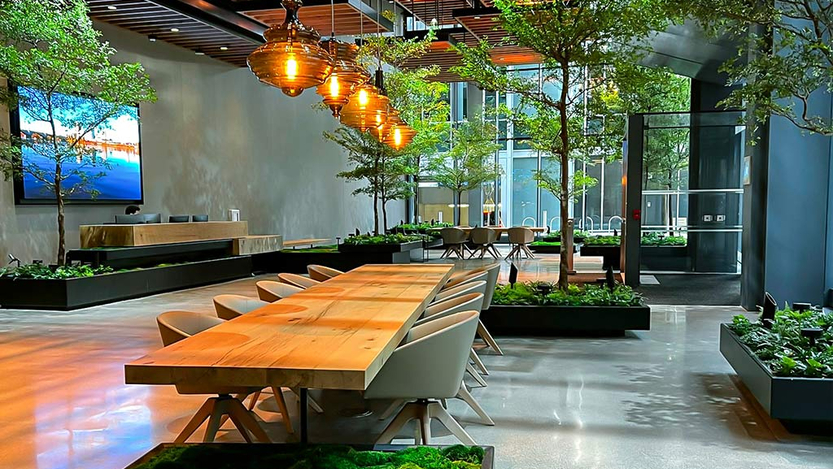
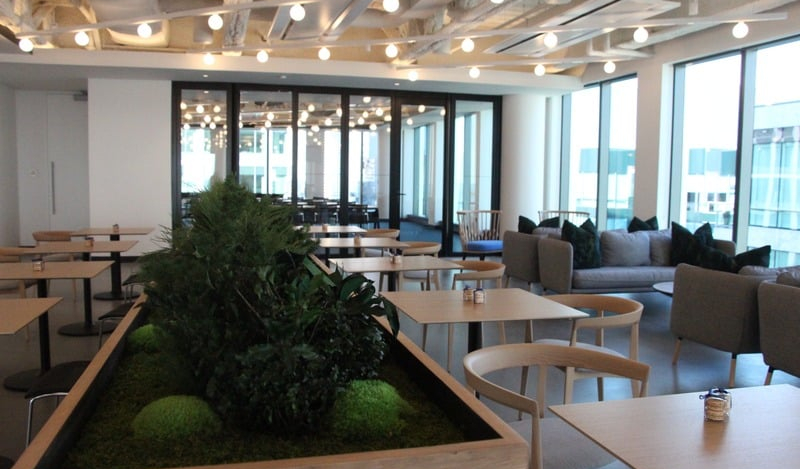
Our new Boston campus opened in November in the Seaport neighborhood.
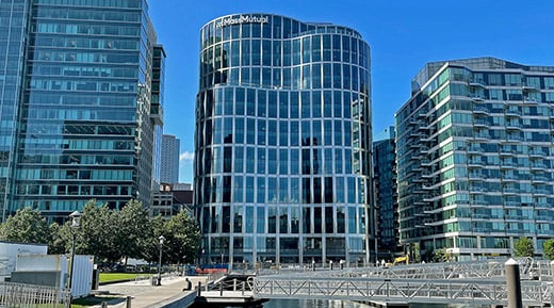
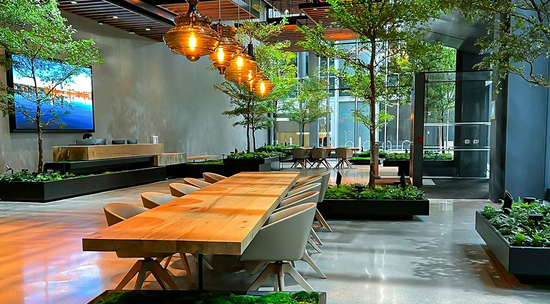
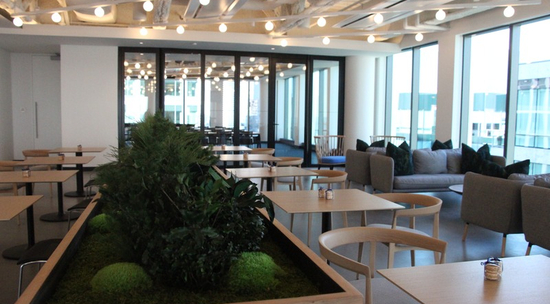

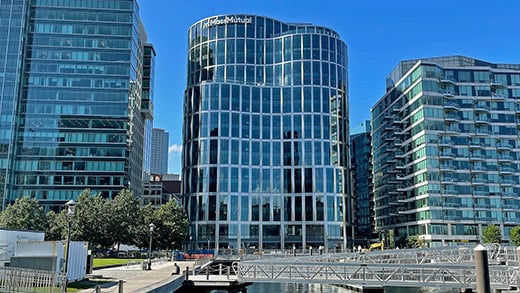
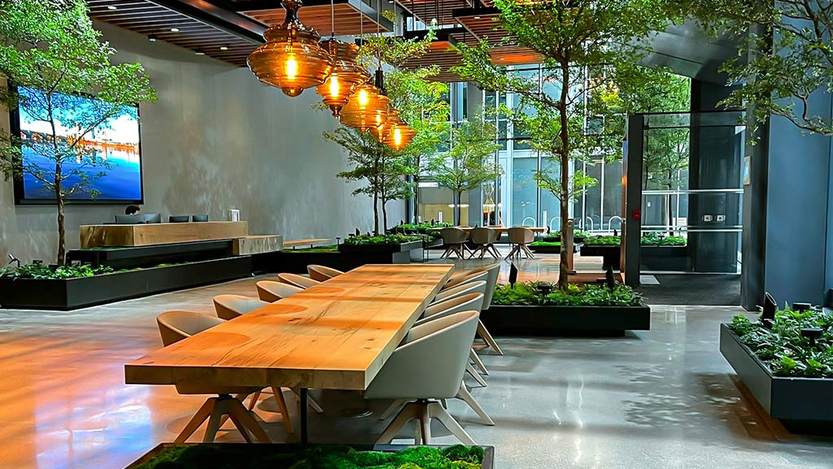
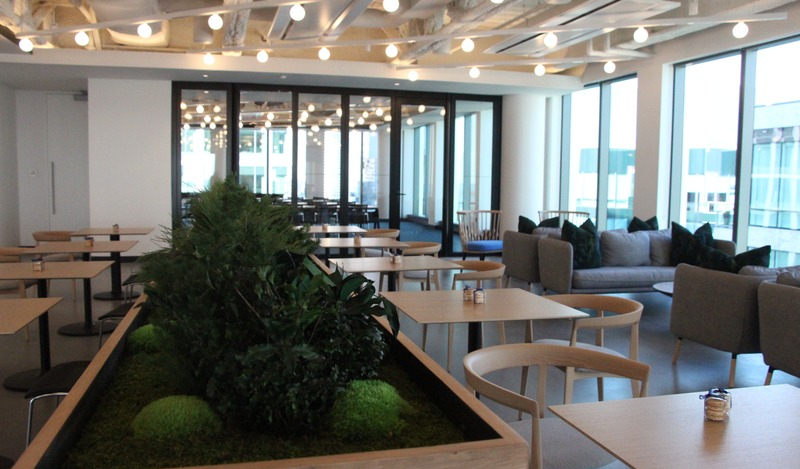

Just like MassMutual, Boston's Seaport district is surrounded by decades of history, yet is now being recognized as a hub for digital innovation and professional growth. With us you can develop the skills you need to build a successful future and connect with talented and collaborative colleagues working together to help people secure their future and protect the ones they love.
Similar Jobs at MassMutual
Big Data • Fintech • Information Technology • Insurance • Financial Services
Participates in MassMutual’s rotational Actuarial Leadership Development Program, supporting actuarial projects across business lines and functions. The role includes mentorship, leadership development, networking with senior actuaries, industry seminars, and corporate learning opportunities. Candidates will apply quantitative and analytical skills, use actuarial modeling platforms, manage projects, and pursue actuarial fellowship while contributing to company initiatives.
Top Skills:
Actuarial Modeling PlatformsExcelProphetVBA
Big Data • Fintech • Information Technology • Insurance • Financial Services
Designs and leads end-to-end business process transformations across Operations, Technology, Risk, Compliance, Legal, and customer experience teams. Responsibilities include current- and future-state process design, Lean analysis, requirements definition, benefit realization, process performance management, automation and AI use-case development, and continuous improvement. The role also establishes process engineering methods, standards, governance, and reusable patterns while influencing senior stakeholders and cross-functional teams without direct authority.
Top Skills:
Artificial IntelligenceAutomationCase-Management ToolsGenesysInsurance Administration SystemsLeanOperational DataProcess ArchitectureProcess MappingSalesforce Financial Services CloudSystems IntegrationValue-Stream AnalysisWorkflow Tools
Big Data • Fintech • Information Technology • Insurance • Financial Services
Manage AI and data science projects from planning through implementation, coordinating technical and non-technical teams, dependencies, Agile ceremonies, requirements, budgets, timelines, scope, and stakeholder expectations. Translate AI capabilities into actionable plans, navigate ambiguity, and drive accountability across multiple teams and priorities.
Top Skills:
Agentic AiAgileConfluenceGenerative AiJIRAMachine Learning
What you need to know about the Boston Tech Scene
Boston is a powerhouse for technology innovation thanks to world-class research universities like MIT and Harvard and a robust pipeline of venture capital investment. Host to the first telephone call and one of the first general-purpose computers ever put into use, Boston is now a hub for biotechnology, robotics and artificial intelligence — though it’s also home to several B2B software giants. So it’s no surprise that the city consistently ranks among the greatest startup ecosystems in the world.
Key Facts About Boston Tech
- Number of Tech Workers: 269,000; 9.4% of overall workforce (2024 CompTIA survey)
- Major Tech Employers: Thermo Fisher Scientific, Toast, Klaviyo, HubSpot, DraftKings
- Key Industries: Artificial intelligence, biotechnology, robotics, software, aerospace
- Funding Landscape: $15.7 billion in venture capital funding in 2024 (Pitchbook)
- Notable Investors: Summit Partners, Volition Capital, Bain Capital Ventures, MassVentures, Highland Capital Partners
- Research Centers and Universities: MIT, Harvard University, Boston College, Tufts University, Boston University, Northeastern University, Smithsonian Astrophysical Observatory, National Bureau of Economic Research, Broad Institute, Lowell Center for Space Science & Technology, National Emerging Infectious Diseases Laboratories
